Corporate networks built on traditional VPN architecture are becoming a liability rather than a safeguard. As organizations expand remote work and cloud adoption, the old model of granting broad network access through a single encrypted tunnel is increasingly mismatched with modern threat environments, where a single compromised credential can expose an entire internal system.
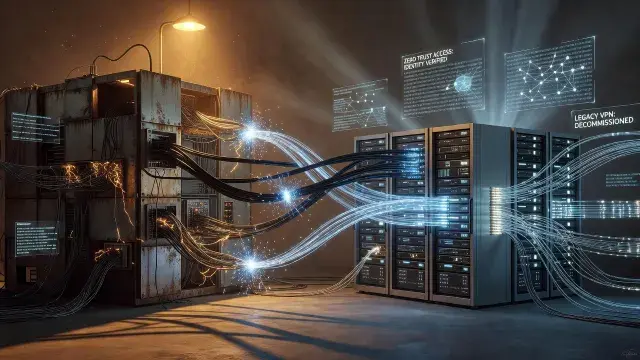
This tension sits at the center of an upcoming webinar, "Under the Hood," scheduled for October 8, which will demonstrate how Check Point's SASE platform implements Zero Trust Network Access (ZTNA) to replace legacy VPN infrastructure. The session promises a practical look at publishing private applications securely and enforcing least-privilege access - principles that have become central to enterprise security planning. For individual users navigating similar access and restriction challenges outside the corporate context, the broader conversation about secure connectivity often leads to the same question consumers face when choosing a provider that handles geo-blocks without compromising on encryption standards or data handling practices.
Why Traditional VPNs Are Losing Ground
Conventional VPNs were designed for a different era, one where most employees worked from a fixed office and the perimeter around a corporate network could be reasonably defended. Once a user authenticates into that VPN, they typically gain access to a wide segment of the internal network, not just the single application they need. This "implicit trust" model creates a structural weakness: if an attacker steals valid credentials or exploits a vulnerable endpoint, lateral movement across the network becomes far easier. Scaling VPN infrastructure for large remote workforces also introduces performance bottlenecks and management complexity that many IT teams struggle to sustain.
What Zero Trust Changes
ZTNA inverts the logic. Instead of granting access to a network, it grants access to a specific application, verified continuously rather than once at login. Every request is evaluated based on identity, device posture, and context, regardless of whether the user is inside or outside the traditional perimeter. Applications are not exposed directly to the internet; they are published through a broker that authenticates each session individually. This approach significantly narrows the attack surface and limits the damage a single compromised account can cause, since access is scoped to least privilege rather than broad network reach.
Implications for Enterprise Security Strategy
The shift toward ZTNA and SASE frameworks reflects a wider industry recognition that perimeter-based security no longer matches how organizations operate. Hybrid work, multi-cloud environments, and increasingly sophisticated credential-based attacks have made identity, not location, the primary security boundary. For security teams, adopting Zero Trust is less about a single product swap and more about redesigning access policy from the ground up. Sessions like the upcoming webinar offer a tangible opportunity to see these architectural changes applied to real infrastructure, rather than treated as abstract policy. For organizations still relying on legacy VPNs, the question is no longer whether to modernize access control, but how quickly the transition can happen without disrupting daily operations.